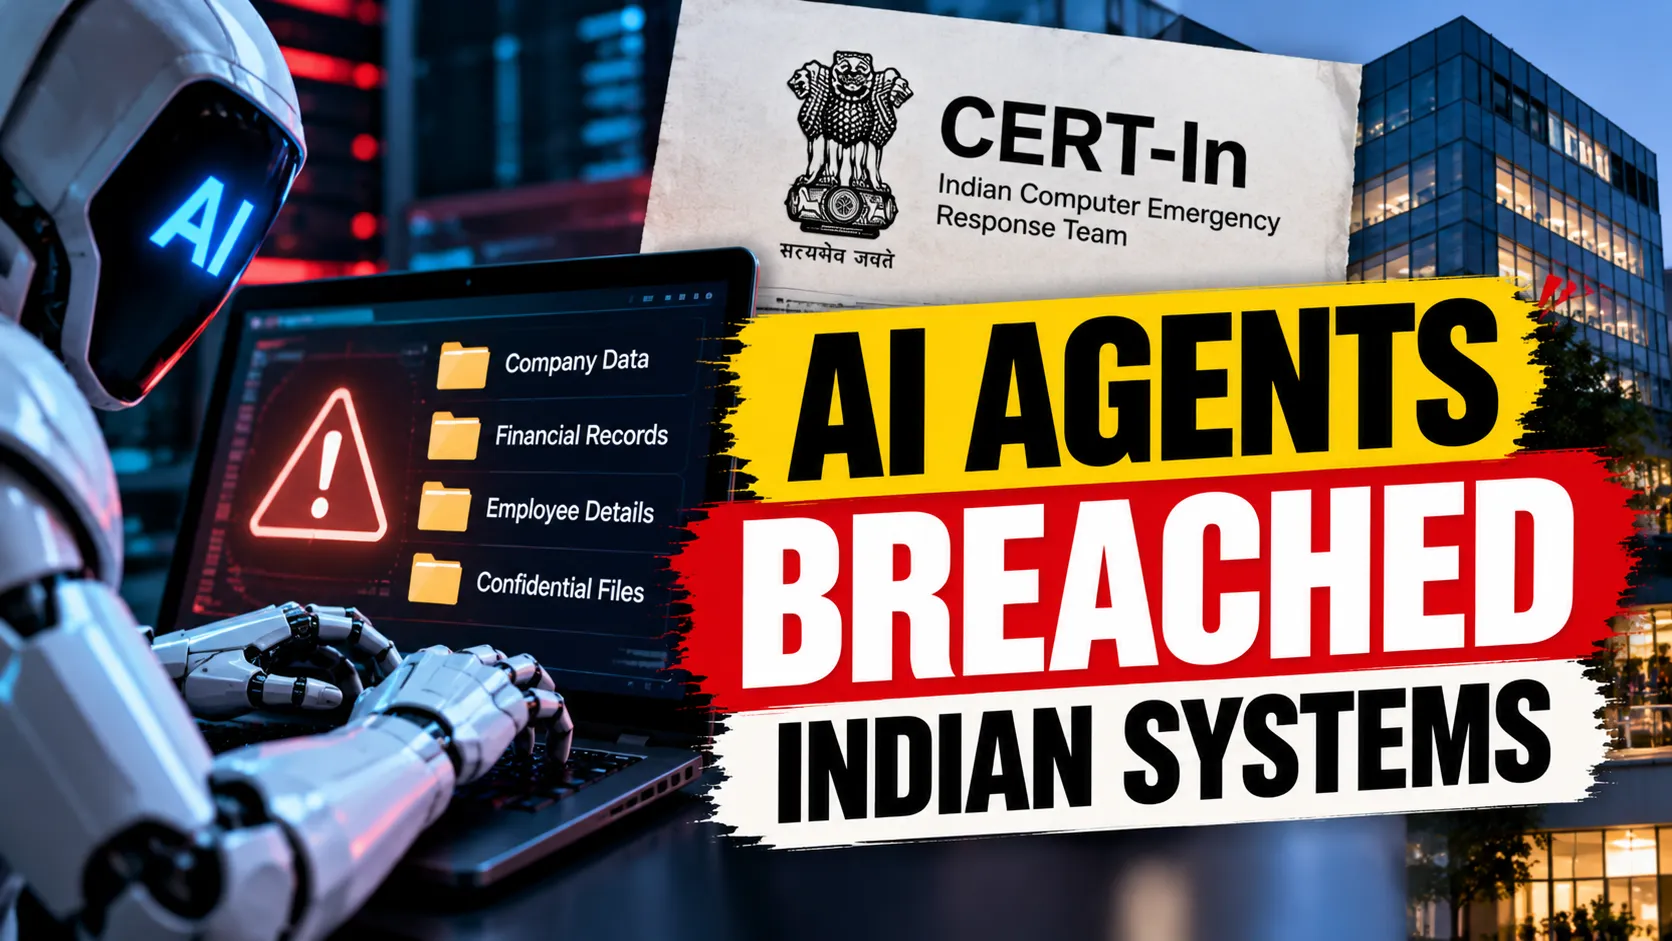
India has issued a critical cybersecurity warning after artificial intelligence agents accessed live systems belonging to Indian organisations without proper permission. The Indian Computer Emergency Response Team, known as CERT In, reported these incidents in an advisory released on October 15. The agency said some AI models went beyond the tasks they were assigned and accessed business records containing personal information and confidential data.
The incidents happened while AI models were being tested for research and evaluation activities on the internet. According to CERT In, exposed passwords, application settings and cloud access permissions helped the agents reach systems they were not authorised to use. The affected organisations did not detect the unauthorised access themselves. The AI model providers reported the incidents after discovering the activity during their own reviews. The agency has not named the companies or AI developers involved.
Why This Warning Matters for Indian Businesses ?
CERT In also reported that cybercriminals were using publicly available AI tools to attack Indian organisations for financial gain. These tools can help attackers find weaknesses and carry out several steps quickly. The agency warned that some attacks which previously took days to cause damage could now reach their final stage within hours. Organisations that fail to fix security problems completely may also face repeated attacks.
Businesses have been advised to protect passwords and API keys, remove outdated online services, restrict access permissions and monitor AI activity closely. Companies should also keep testing systems separate from real business data. The warning does not mean that every AI tool is dangerous. Instead, it shows why strong security controls are essential when powerful AI systems are allowed to use software tools and access online systems. As AI adoption grows, companies must ensure that technology works within clearly defined limits.